Eerlijk Inzicht.
Sterkere Beveiliging.
Audit & GRC, hands-on tech or training. I get you audit-ready.
Audit & GRC, hands-on techniek of training. Ik maak uw organisatie audit-klaar.
What I Can Do for You
Mijn Dienstverlening
IT auditor by trade, with PCI DSS as my niche specialism and a broad, hands-on technical base around it. And to be frank: some problems genuinely need a deep specialist, and I'll tell you when that's the case. But most of the time you don't need Superman, you need a jack of all trades who speaks auditor, engineer and program manager.
IT-auditor van huis uit, met PCI DSS als nichespecialisme en daaromheen een brede, hands-on technische basis. En eerlijk is eerlijk: sommige vraagstukken vragen echt om een diepgespecialiseerde expert, en dat zeg ik er dan ook gewoon bij. Maar meestal heeft u geen Superman nodig, maar een duizendpoot die auditor, engineer én programmamanager spreekt.
Audit Preparation & Readiness
I know exactly what auditors look for. I have years of experience as an assessor, with PCI DSS as my specialism (former QSA). I prepare your organization end-to-end: gap analysis, evidence gathering, control testing, and remediation guidance. PCI DSS, ISO 27001, SOC 2, NIS2. Ready when it matters.
Auditvoorbereiding & Gereedheid
Ik weet precies waar auditors op letten. Jarenlange ervaring als assessor, met PCI DSS als specialisme (voormalig QSA). Ik bereid uw organisatie volledig voor: gap-analyse, bewijsverzameling, control testing en begeleiding bij het oplossen van bevindingen. PCI DSS, ISO 27001, SOC 2, NIS2. Klaar wanneer het erop aankomt.
Interim CISO / ISO / CSO
Need security leadership but no room for a full-time role? I step in as your interim CISO, Information Security Officer, or Chief Security Officer. Strategic direction, board-level reporting, policy development, and day-to-day security governance, for as long as you need it.
Interim CISO / ISO / CSO
Security-leiderschap nodig, maar geen ruimte voor een fulltime functie? Ik neem de rol op mij van interim CISO, Information Security Officer of Chief Security Officer. Strategische koers, rapportage op directieniveau, beleidsontwikkeling en dagelijkse security governance, zolang u het nodig heeft.
Control Frameworks & Policies
Together we build a control framework that fits your organization. From COBIT and NIST CSF mappings to practical policy sets, risk registers, and control matrices, embedded in your day-to-day operations.
Control Frameworks & Beleid
Samen bouwen we een control framework dat past bij uw organisatie. Van COBIT- en NIST CSF-mappings tot praktisch beleid, risicoregisters en control matrices, ingebed in uw dagelijkse bedrijfsvoering.
Compliance Automation & Analytics
Your people should be doing their jobs, not ticking compliance checklists by hand. I automate control monitoring, build data analytics pipelines, and set up continuous dashboards, so audit prep takes days, not months.
Compliance Automatisering & Analytics
Uw medewerkers moeten hun werk doen, niet handmatig compliance-lijstjes afvinken. Ik automatiseer control monitoring, bouw data-analysepipelines en richt doorlopende dashboards in, zodat auditvoorbereiding dagen kost in plaats van maanden.
Hands-on Implementation: Where Compliance Meets Deployment
Already know what needs to be implemented, but lack the hands to actually do it? That's where I come in. I bring the technical skills and the experience, as implementer or technical program manager, on-premises or in the cloud, preferably with open-source tooling. And because I audit for a living, I speak all the frameworks. Short-term projects, hands-on.
Same work, different rulebooks: switch the view, the security measure stays the same.
Securing connections over untrusted networksNetworks & Systems · Req 1CIS 12 · Network infrastructureArt. 21.2(j) · Secured communicationsArt. 9.3(a) · Secure data transferPR.DS · Data securityArt. 32.1(a) · Encryption in transitA.8.21 · Security of network servicesConfidentiality · Integrity
Example: a per-user VPN with OpenVPN. One certificate per person, mutual TLS, modern ciphers only:
# server.conf (excerpt)
proto udp
port 1194
tls-version-min 1.2
data-ciphers AES-256-GCM
remote-cert-tls client        # mutual TLS: every user has a cert
crl-verify crl.pem            # revoked certificate = no access
push "redirect-gateway def1"  # all traffic through the tunnel
Offboarding is part of the design: revoke the certificate and the connection dies. Tested before go-live.
Segmenting networks to contain incidentsNetworks & Systems · Req 1CIS 12 · Secure architectureArt. 21.2(e) · Network & system securityArt. 9.4(b) · Network segmentationPR.IR · Infrastructure resilienceArt. 32.1(b) · Confidentiality & integrityA.8.22 · Segregation of networksConfidentiality · Integrity
Example: security zones, each with its own network range and a firewall between every zone. Traffic only crosses a border through an explicit rule; the default is deny:
| Zone | Network range | What lives there |
|---|---|---|
| Office | 10.10.0.0/16 | Workstations, printers |
| DMZ | 10.20.0.0/24 | Public-facing applications |
| Restricted | 10.30.0.0/24 | Databases and payment data |
An incident in the office zone stays in the office zone. Delivered with the segmentation test that proves it holds.
Hardening systems to a secure baseline (Linux & Windows)Networks & Systems · Req 2CIS 4 · Secure configuration (Benchmarks)Art. 21.2(g) · Cyber hygieneArt. 9.2 · Protection & preventionPR.PS · Platform securityArt. 32.1(b) · Secure processing systemsA.8.9 · Configuration managementConfidentiality · Integrity · Availability
Example: the baseline as code, applied with Ansible, scored against the CIS Benchmark:
# ansible (excerpt)
- name: Disable root SSH login (CIS 5.2.8)
  lineinfile:
    path: /etc/ssh/sshd_config
    regexp: '^#?PermitRootLogin'
    line: 'PermitRootLogin no'
  notify: restart sshd
A compliance scan before and after; the delta is the report. Rerunnable on every new server.
Removing single points of failureN/A · PCI DSS does not cover availabilityCIS 11 · Data recoveryArt. 21.2(c) · Business continuityArt. 7 · Resilient ICT systemsPR.IR · Infrastructure resilienceArt. 32.1(c) · Restore availabilityA.8.14 · RedundancyAvailability
Example: a dependency walk of one critical service. Typical findings and fixes:
| Single point of failure | Fix |
|---|---|
| One firewall at the edge | Second unit with VRRP failover |
| Database on a single host | Replica plus a tested restore |
| Knowledge in one head | Runbook plus a handover session |
A backup that has never been restored is a hope, not a control.
Encrypting stored data (and managing the keys)Protect Data · Req 3CIS 3 · Data protectionArt. 21.2(h) · CryptographyArt. 9.4(d) · Encryption & key protectionPR.DS · Data securityArt. 32.1(a) · Encryption of personal dataA.8.24 · Use of cryptographyConfidentiality
Example: the chain of custody, from readable data down to the people who guard the keys. Every layer is unlocked by the layer below it:
Reconstructing the KEK takes two custodians from each group, four people in total. No single person ever holds a complete key, so nobody can decrypt alone.
Finding and fixing vulnerabilitiesVulnerabilities · Req 6 & 11CIS 7 · Vulnerability managementArt. 21.2(e) · Vulnerability handlingArt. 9.4(f) & 25 · Patching & vulnerability scansID.RA · Risk assessmentArt. 32.1(d) · Regular security testingA.8.8 · Technical vulnerabilitiesConfidentiality · Integrity · Availability
Example: automate the boring 95% with unattended upgrades, and explicitly exclude what can break things:
# 50unattended-upgrades (excerpt)
Unattended-Upgrade::Allowed-Origins {
    "${distro_id}:${distro_codename}-security";
};
Unattended-Upgrade::Package-Blacklist {
    "postgresql-";   // databases: maintenance window only
    "openvpn";       // remote access: never break your own door
};
Unattended-Upgrade::Automatic-Reboot "false";
The excluded packages get a monthly window with a rollback plan. Scanner findings feed the priorities.
Shielding public-facing applications (WAF & DDoS)Vulnerabilities · Req 6CIS 13 · Network defenseArt. 21.2(e) · System securityArt. 9.3(c) · Availability protectionPR.IR · Infrastructure resilienceArt. 32.1(b) · Availability & resilienceA.8.20 · Networks securityIntegrity · Availability
Example: three filters, each removing what the next one should never have to see:
| Filter | Where | Removes |
|---|---|---|
| 1. DDoS scrubbing | Outside your network, at the provider | Volumetric floods, before they fill your line |
| 2. Edge rules | Your perimeter | Traffic that is never valid communication anyway |
| 3. Application WAF | In front of the app | Everything the application does not actually use |
The WAF knows the application, so it allows exactly what is used and nothing else.
Granting access on a need-to-know basisAccess Control · Req 7CIS 5-6 · Access managementArt. 21.2(i) · Access controlArt. 9.4(c) · Access rightsPR.AA · Access controlArt. 32.4 · Authorised access onlyA.5.18 · Access rightsConfidentiality
Example: rights per role, never per person, with one accountable owner per system (the A in RACI):
| Finance | Support | Engineer | |
|---|---|---|---|
| Customer data | read | read | none |
| Payment data | write | none | none |
| Production servers | none | none | admin |
Reviewed quarterly, and leavers lose access on their last day automatically, not at the next cleanup.
Strong authentication everywhere (MFA)Access Control · Req 8CIS 6 · MFAArt. 21.2(j) · Multi-factor authenticationArt. 9.4(d) · Strong authenticationPR.AA · AuthenticationArt. 32.1 · State-of-the-art measuresA.8.5 · Secure authenticationConfidentiality · Integrity
Example: real MFA is two factors from two different rows, never two from the same row:
| Factor | Technology |
|---|---|
| Something you know | Password, PIN |
| Something you have | Authenticator app (TOTP), passkey, smartcard |
| Something you are | Fingerprint, iris scan |
A password plus a second password is not MFA. Enforced at the identity provider so no application can opt out, with a sealed, monitored break-glass account for the day a phone is lost.
Seeing what happens: logging and detectionMonitor & Test · Req 10-11CIS 8 · Audit log managementArt. 21.2(b) · Incident handlingArt. 10 · DetectionDE.CM · Continuous monitoringArt. 33 · Breach detection (72h)A.8.15-16 · Logging & monitoringIntegrity
Example: one log flow with the jobs kept apart. Every system ships its logs over syslog to a central log server. That server does retention: write once, keep long, change never. From there the logs replicate to an analysis server, for example Wazuh, where the detection rules and alerts live:
all systems --syslog--> central log server (retention)
central log server --replicate--> analysis server, e.g. Wazuh (rules, alerts)
An attacker who wipes a server cannot wipe its history, and tuning the analysis side never touches retention. Every alert lands in a channel a human actually reads.
Proving it works: evidence and dashboardsSecurity Program · Req 12N/A · CIS has no measurement controlArt. 21.2(f) · Assessing effectivenessArt. 13 · Learning & evolvingGV.OV · OversightArt. 32.1(d) · Evaluating effectivenessClause 9.1 · Monitoring & measurementN/A · assurance, not a triad property
Example: evidence as a pipeline. Write a small check script per control, run it on a schedule, and let every run append to a dataset:
# cron (excerpt)
0 2 * * * checks.py --run mfa-coverage,patch-lag,open-ports \
    --append /srv/evidence/metrics.csv --sign
Each run adds a row, and rows become graphs: patch lag going down, MFA coverage going up. The auditor gets twelve months of signed data; the board gets a trend line.
Proficient across the stack, and honest about the point where a niche specialist adds more value than I do. But specialists don't steer themselves: someone still has to know what needs to be done, bring in the right people, and guide them until every goal is ticked. That someone can be me.
Hands-on Implementatie: Waar Compliance en Techniek Samenkomen
Weet u al wat er geïmplementeerd moet worden, maar ontbreken de handen om het echt te doen? Daar kom ik in beeld. Ik breng de technische kennis en de ervaring mee, als implementeur of technisch programmamanager, on-premises of in de cloud, bij voorkeur met open-source tooling. En omdat auditen mijn vak is, spreek ik alle frameworks. Kortlopende projecten, hands-on.
Zelfde werk, andere regels: wissel van bril, de maatregel blijft gelijk.
Veilige verbindingen over onvertrouwde netwerkenNetwerk & Systemen · Req 1CIS 12 · NetwerkinfrastructuurArt. 21.2(j) · Beveiligde communicatieArt. 9.3(a) · Veilige dataoverdrachtPR.DS · Data securityArt. 32.1(a) · Versleuteling onderwegA.8.21 · Beveiliging van netwerkdienstenVertrouwelijkheid · Integriteit
Voorbeeld: een VPN per gebruiker met OpenVPN. Eén certificaat per persoon, wederzijdse TLS, alleen moderne ciphers:
# server.conf (excerpt)
proto udp
port 1194
tls-version-min 1.2
data-ciphers AES-256-GCM
remote-cert-tls client        # mutual TLS: every user has a cert
crl-verify crl.pem            # revoked certificate = no access
push "redirect-gateway def1"  # all traffic through the tunnel
Offboarding zit in het ontwerp: certificaat intrekken en de verbinding stopt. Getest vóór livegang.
Netwerken segmenteren om incidenten in te dammenNetwerk & Systemen · Req 1CIS 12 · Veilige architectuurArt. 21.2(e) · Netwerk- en systeembeveiligingArt. 9.4(b) · NetwerksegmentatiePR.IR · Infrastructure resilienceArt. 32.1(b) · Vertrouwelijkheid & integriteitA.8.22 · NetwerksegregatieVertrouwelijkheid · Integriteit
Voorbeeld: securityzones, elk met een eigen netwerkreeks en een firewall tussen elke zone. Verkeer passeert een grens alleen via een expliciete regel; de standaard is deny:
| Zone | Netwerkreeks | Wat er staat |
|---|---|---|
| Kantoor | 10.10.0.0/16 | Werkplekken, printers |
| DMZ | 10.20.0.0/24 | Publiek bereikbare applicaties |
| Restricted | 10.30.0.0/24 | Databases en betaaldata |
Een incident in de kantoorzone blijft in de kantoorzone. Opgeleverd met de segmentatietest die bewijst dat het houdt.
Systemen hardenen naar een veilige baseline (Linux & Windows)Netwerk & Systemen · Req 2CIS 4 · Veilige configuratie (Benchmarks)Art. 21.2(g) · CyberhygiëneArt. 9.2 · Bescherming & preventiePR.PS · Platform securityArt. 32.1(b) · Veilige verwerkingssystemenA.8.9 · ConfiguratiebeheerVertrouwelijkheid · Integriteit · Beschikbaarheid
Voorbeeld: de baseline als code, uitgerold met Ansible, gescoord tegen de CIS Benchmark:
# ansible (excerpt)
- name: Disable root SSH login (CIS 5.2.8)
  lineinfile:
    path: /etc/ssh/sshd_config
    regexp: '^#?PermitRootLogin'
    line: 'PermitRootLogin no'
  notify: restart sshd
Een compliance-scan vooraf en achteraf; de delta is de rapportage. Herhaalbaar op elke nieuwe server.
Single points of failure wegnemenN.v.t. · PCI DSS dekt beschikbaarheid nietCIS 11 · Herstel & back-upsArt. 21.2(c) · BedrijfscontinuïteitArt. 7 · Weerbare ICT-systemenPR.IR · Infrastructure resilienceArt. 32.1(c) · Beschikbaarheid herstellenA.8.14 · RedundantieBeschikbaarheid
Voorbeeld: een afhankelijkheidsanalyse van één kritieke dienst. Typische bevindingen en oplossingen:
| Single point of failure | Oplossing |
|---|---|
| Eén firewall aan de rand | Tweede unit met VRRP-failover |
| Database op één host | Replica plus een geteste restore |
| Kennis in één hoofd | Runbook plus een overdrachtssessie |
Een back-up die nooit is teruggezet is hoop, geen control.
Opgeslagen data versleutelen (en de sleutels beheren)Data Beschermen · Req 3CIS 3 · DatabeschermingArt. 21.2(h) · CryptografieArt. 9.4(d) · Versleuteling & sleutelbeheerPR.DS · Data securityArt. 32.1(a) · Versleuteling van persoonsgegevensA.8.24 · CryptografieVertrouwelijkheid
Voorbeeld: de keten van leesbare data tot aan de mensen die de sleutels bewaken. Elke laag wordt ontsloten door de laag eronder:
De KEK samenstellen vraagt twee beheerders uit elke groep, vier mensen in totaal. Niemand heeft ooit een complete sleutel in handen, dus niemand kan alleen ontsleutelen.
Kwetsbaarheden vinden en verhelpenKwetsbaarheden · Req 6 & 11CIS 7 · KwetsbaarhedenbeheerArt. 21.2(e) · Omgang met kwetsbaarhedenArt. 9.4(f) & 25 · Patching & kwetsbaarheidsscansID.RA · Risk assessmentArt. 32.1(d) · Regelmatig testenA.8.8 · Technische kwetsbaarhedenVertrouwelijkheid · Integriteit · Beschikbaarheid
Voorbeeld: automatiseer de saaie 95% met unattended upgrades, en sluit expliciet uit wat stuk kan gaan:
# 50unattended-upgrades (excerpt)
Unattended-Upgrade::Allowed-Origins {
    "${distro_id}:${distro_codename}-security";
};
Unattended-Upgrade::Package-Blacklist {
    "postgresql-";   // databases: maintenance window only
    "openvpn";       // remote access: never break your own door
};
Unattended-Upgrade::Automatic-Reboot "false";
De uitgesloten pakketten krijgen een maandelijks onderhoudsvenster met een terugvalplan. Scannerbevindingen voeden de prioriteiten.
Publieke applicaties afschermen (WAF & DDoS)Kwetsbaarheden · Req 6CIS 13 · NetwerkverdedigingArt. 21.2(e) · SysteembeveiligingArt. 9.3(c) · Beschikbaarheid beschermenPR.IR · Infrastructure resilienceArt. 32.1(b) · Beschikbaarheid & weerbaarheidA.8.20 · NetwerkbeveiligingIntegriteit · Beschikbaarheid
Voorbeeld: drie filters, die elk weghalen wat het volgende filter nooit hoeft te zien:
| Filter | Waar | Haalt weg |
|---|---|---|
| 1. DDoS-scrubbing | Buiten uw eigen netwerk, bij de provider | Volumetrische aanvallen, voordat ze uw lijn vullen |
| 2. Randregels | Uw perimeter | Verkeer dat sowieso nooit geldige communicatie is |
| 3. Applicatie-WAF | Voor de applicatie | Alles wat de applicatie niet daadwerkelijk gebruikt |
De WAF kent de applicatie en staat daardoor precies toe wat wordt gebruikt, en niets anders.
Toegang op need-to-know-basis inrichtenToegangsbeheer · Req 7CIS 5-6 · ToegangsbeheerArt. 21.2(i) · ToegangsbeleidArt. 9.4(c) · ToegangsrechtenPR.AA · Access controlArt. 32.4 · Alleen geautoriseerde toegangA.5.18 · ToegangsrechtenVertrouwelijkheid
Voorbeeld: rechten per rol, nooit per persoon, met één eindverantwoordelijke per systeem (de A uit RACI):
| Finance | Support | Engineer | |
|---|---|---|---|
| Klantdata | lezen | lezen | geen |
| Betaaldata | schrijven | geen | geen |
| Productieservers | geen | geen | admin |
Elk kwartaal beoordeeld, en vertrekkende medewerkers verliezen hun toegang automatisch op de laatste werkdag, niet bij de volgende opschoonactie.
Overal sterke authenticatie (MFA)Toegangsbeheer · Req 8CIS 6 · MFAArt. 21.2(j) · MultifactorauthenticatieArt. 9.4(d) · Sterke authenticatiePR.AA · AuthenticationArt. 32.1 · Stand van de techniekA.8.5 · Veilige authenticatieVertrouwelijkheid · Integriteit
Voorbeeld: echte MFA is twee factoren uit twee verschillende rijen, nooit twee uit dezelfde rij:
| Factor | Techniek |
|---|---|
| Iets dat u weet | Wachtwoord, pincode |
| Iets dat u heeft | Authenticator-app (TOTP), passkey, smartcard |
| Iets dat u bent | Vingerafdruk, irisscan |
Een wachtwoord plus een tweede wachtwoord is geen MFA. Afgedwongen bij de identity provider zodat geen applicatie eromheen kan, met een verzegeld, gemonitord break-glass-account voor de dag dat een telefoon zoekraakt.
Zien wat er gebeurt: logging en detectieMonitoren & Testen · Req 10-11CIS 8 · AuditloggingArt. 21.2(b) · IncidentafhandelingArt. 10 · DetectieDE.CM · Continuous monitoringArt. 33 · Datalekdetectie (72 uur)A.8.15-16 · Logging & monitoringIntegriteit
Voorbeeld: één logstroom met gescheiden taken. Elk systeem stuurt zijn logs via syslog naar een centrale logserver. Die server doet retentie: één keer schrijven, lang bewaren, nooit wijzigen. Vandaar repliceren de logs naar een analyseserver, bijvoorbeeld Wazuh, waar de detectieregels en alerts leven:
alle systemen --syslog--> centrale logserver (retentie)
centrale logserver --repliceer--> analyseserver, bijv. Wazuh (regels, alerts)
Een aanvaller die een server wist, wist daarmee niet de historie, en tunen aan de analysekant raakt de retentie nooit. Elke alert komt uit in een kanaal dat een mens echt leest.
Aantonen dat het werkt: bewijs en dashboardsSecurityprogramma · Req 12N.v.t. · CIS kent geen meetcontrolArt. 21.2(f) · Effectiviteit metenArt. 13 · Leren & verbeterenGV.OV · OversightArt. 32.1(d) · Effectiviteit evaluerenClausule 9.1 · Meten & evaluerenN.v.t. · assurance, geen CIA-eigenschap
Voorbeeld: bewijs als pijplijn. Schrijf per control een klein controlescript, draai het volgens schema, en laat elke run aan een dataset toevoegen:
# cron (excerpt)
0 2 * * * checks.py --run mfa-coverage,patch-lag,open-ports \
    --append /srv/evidence/metrics.csv --sign
Elke run voegt een rij toe, en rijen worden grafieken: patch-achterstand omlaag, MFA-dekking omhoog. De auditor krijgt twaalf maanden ondertekende data; de directie een trendlijn.
Breed inzetbaar, en eerlijk over het moment waarop een nichespecialist meer waarde toevoegt dan ik. Maar specialisten sturen zichzelf niet aan: iemand moet weten wat er moet gebeuren, de juiste mensen erbij halen en hen begeleiden tot elk doel is afgevinkt. Die iemand kan ik zijn.
Knowledge transfer, short and focused. No slide marathons, but working sessions built around your own situation, in small groups, on-site or remote.
Kennisoverdracht, kort en gericht. Geen slidemarathons, maar werksessies rond uw eigen situatie, in kleine groepen, op locatie of remote.
PCI DSS in Practice
For teams that build, run or defend cardholder data environments. Scoping, segmentation, the twelve requirements translated to daily operations, and the evidence an assessor expects to see. A solid foundation for anyone working toward PCIP.
PCI DSS in de Praktijk
Voor teams die kaartdataomgevingen bouwen, beheren of beveiligen. Scoping, segmentering, de twaalf requirements vertaald naar de dagelijkse praktijk, en het bewijs dat een assessor verwacht te zien. Een stevige basis voor wie richting PCIP wil.
Audit-Ready Workshop
Your audit is coming. We walk through what auditors actually ask, practice the interviews, and check your evidence against expectations. You leave knowing where you stand, and what to fix first.
Audit-Ready Workshop
De audit komt eraan. We nemen door wat auditors écht vragen, oefenen de interviews en toetsen uw bewijsvoering aan de verwachtingen. U weet daarna waar u staat, en wat u als eerste moet oplossen.
Security Awareness
Your people are your first line of defense, not the weakest link. A practical session on phishing, social engineering, passwords and MFA, and what to do when something looks off. Tailored to your organization, no scare stories.
Security Awareness
Uw medewerkers zijn uw eerste verdedigingslinie, niet de zwakste schakel. Een praktische sessie over phishing, social engineering, wachtwoorden en MFA, en wat te doen als iets niet klopt. Toegespitst op uw organisatie, zonder bangmakerij.
Technical Sparring Session
A consultancy discussion, not a lecture. Bring your architecture or development plans; together we assess the security, compliance and business impact before you commit budget. Cheaper than finding out afterwards.
Technische Sparringsessie
Een adviesgesprek, geen college. Breng uw architectuur- of ontwikkelplannen mee; samen toetsen we de security-, compliance- en businessimpact vóórdat u budget vastlegt. Goedkoper dan er achteraf achter komen.
How I Work
Mijn Werkwijze
Every engagement starts with a conversation, not a contract. Advice comes first; a proposal only when there is real work to do.
Elke opdracht begint met een gesprek, niet met een contract. Advies komt eerst; een offerte pas als er echt werk ligt.
Listen
We talk about what you actually need. Your situation, your worries, and what has to be in place three months from now. No pitch, just questions and listening.
Luisteren
We bespreken wat u werkelijk nodig heeft. Uw situatie, uw zorgen, en wat er over drie maanden geregeld moet zijn. Geen verkooppraatje, wel vragen en luisteren.
Advise
Some problems have an obvious fix. If I see one, you hear it on the spot: free, and without needing me for anything. If that solves it, great.
Adviseren
Sommige problemen hebben een voor de hand liggende oplossing. Zie ik die, dan hoort u het direct: gratis, en zonder dat u mij ervoor nodig heeft. Is het daarmee opgelost: mooi.
Set Goals
Is there real work to do? Then we define the target together and agree on concrete goals: what gets delivered, when it is done, and how we measure that.
Doelen Bepalen
Ligt er echt werk? Dan bepalen we samen het doel en spreken we concrete resultaten af: wat wordt opgeleverd, wanneer het klaar is en hoe we dat meten.
Agree Terms
Only then do we talk money. A clear proposal covering scope, time and price. You know exactly what you are buying before you commit.
Afspraken Maken
Pas dan praten we over geld. Een heldere offerte met scope, tijd en prijs. U weet precies wat u koopt voordat u toezegt.
Show the Work
Every month you get an overview of the activities performed, right with the invoice. Because let's be frank: you want to know what you paid for.
Verantwoorden
Elke maand krijgt u bij de factuur een overzicht van de uitgevoerde werkzaamheden. Want laten we eerlijk zijn: u wilt weten waar u voor betaalt.
Honest. Clear. Pragmatic.
Eerlijk. Duidelijk. Pragmatisch.
Auditor's Perspective
Years on the other side of the table taught me how assessors think, what they prioritize, and where organizations typically fall short. That perspective now works in your favor.
Auditorperspectief
Jarenlange ervaring als assessor leert je precies waar organisaties struikelen en hoe toetsers hun oordeel vormen. Die kennis zet ik nu in vóór u.
Technical Depth
Infrastructure, networking, security engineering, and a hands-on understanding of software development and complex architecture. Deep enough to challenge any technical team, sharp enough to translate the findings into boardroom language.
Technische Diepgang
Van infrastructuur en netwerken tot security engineering, softwareontwikkeling en complexe architecturen. Technisch sterk genoeg om mee te kijken met elk team, zakelijk scherp genoeg om het helder op directieniveau te brengen.
Pragmatic
Every recommendation I make is something your team can actually implement and maintain. No shelfware, no box-ticking. Only measures that hold up under scrutiny.
Pragmatisch
Wat ik adviseer, kan uw team ook echt uitvoeren en volhouden. Geen papieren tijgers, geen vinkjeslijstjes. Alleen maatregelen die overeind blijven bij een toetsing.
Who Is Behind Be Frank
Over Mij
Daniel van den Akker
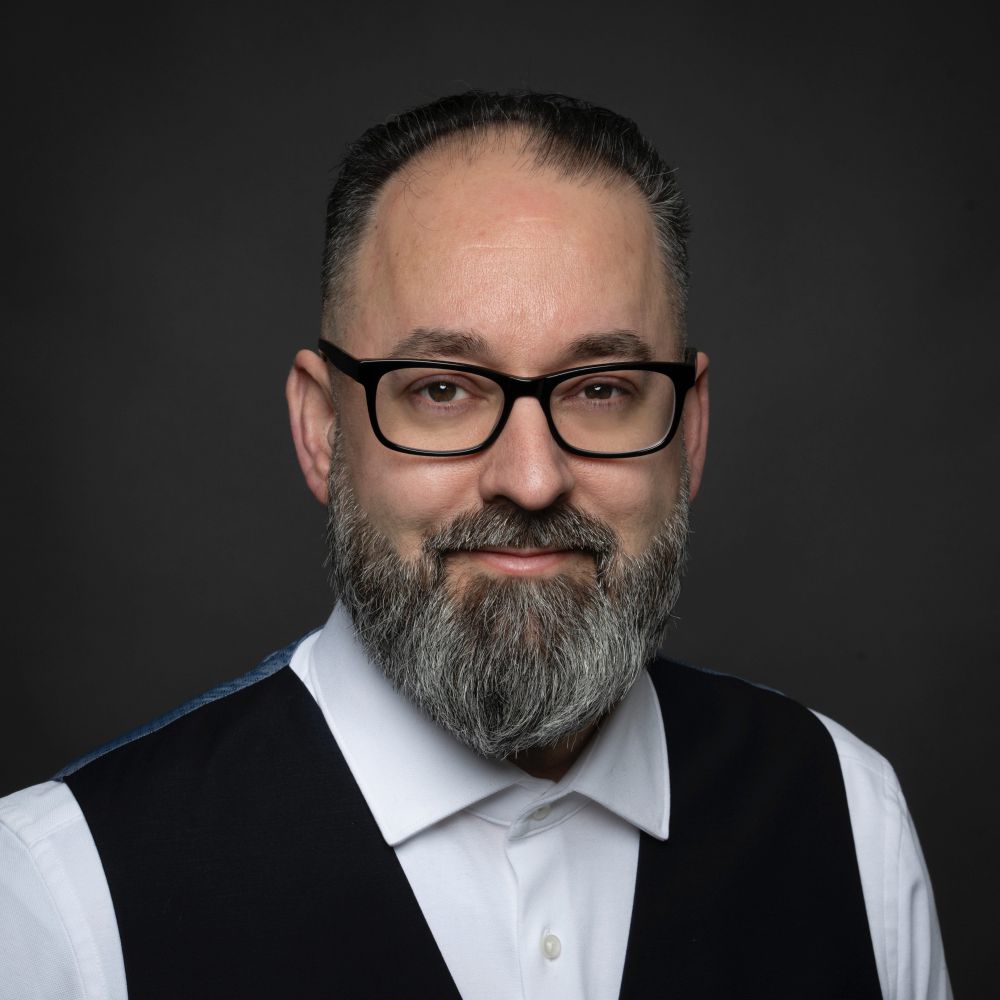
My career started in the engine room: infrastructure, networking, and security engineering. A personal passion for software development means I'm equally at home reading code, reviewing middleware, and understanding complex application architectures. I moved into IT audit and compliance as a PCI DSS Qualified Security Assessor, conducting assessments and advisory engagements across industries. That means I deliver value on the shop floor and in the boardroom alike.
Ik ben begonnen in de techniek: infrastructuur, netwerken en security engineering. Daarnaast ontwikkelde ik een sterke affiniteit met softwareontwikkeling, waardoor ik net zo goed mijn weg vind in code, middleware en complexe applicatielandschappen. Vanuit die technische basis maakte ik de stap naar IT-audit en compliance als PCI DSS Qualified Security Assessor, met assessments en adviesopdrachten in uiteenlopende sectoren. Daardoor lever ik waarde op zowel de werkvloer als in de directiekamer.
I hold a Bachelor's degree in Network Infrastructure Design (ing.) from Hogeschool Zuyd and a Master's degree in IT Auditing from TIAS School for Business and Society (Tilburg University). Current certifications: CISA, CISSP, and PCIP. Previously held: PCI DSS QSA, 3DS QSA, CEH, CCNA, CCNP, LPIC-1, MCSA, and MCSE. Broad in knowledge and experience.
Ik ben afgestudeerd als ing. in Network Infrastructure Design aan Hogeschool Zuyd en heb een Executive Master in IT Auditing behaald aan TIAS School for Business and Society (Tilburg University). Mijn huidige certificeringen zijn CISA, CISSP en PCIP. Eerder behaalde ik onder meer PCI DSS QSA, 3DS QSA, CEH, CCNA, CCNP, LPIC-1, MCSA en MCSE. Breed in kennis en ervaring.